

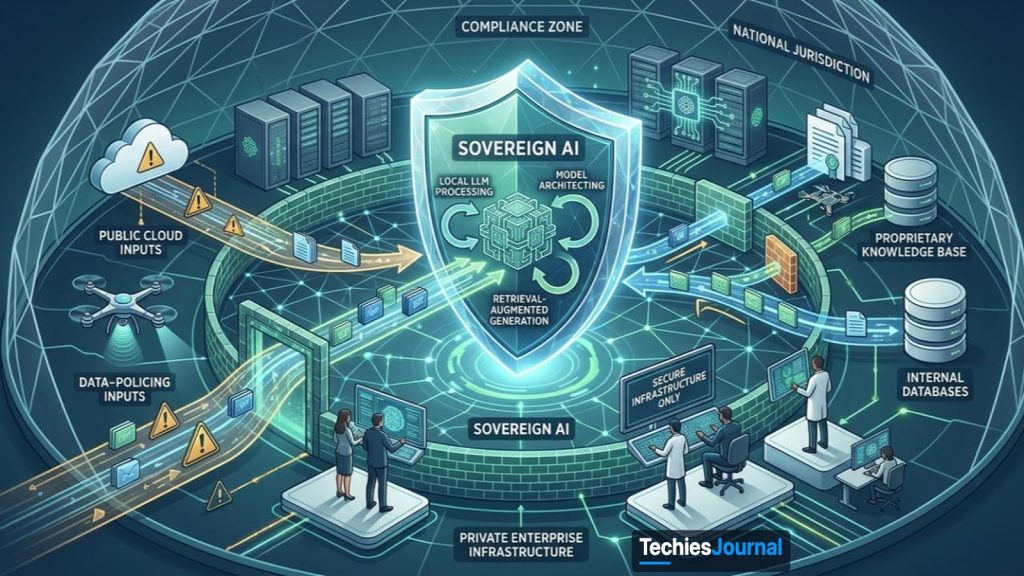
October 2026 announcements from Google, Microsoft, IBM and AWS show how sovereign AI infrastructure is evolving. The practical challenge is determining where models run, who controls the environment and which dependencies remain.
A regulated organization wants an AI assistant to search confidential reports and internal documents.
It stores all the files in an approved country. But the assistant sends requests to an AI model hosted elsewhere, uses an external identity provider and depends on remote administrators to maintain its infrastructure.
The data may be stored locally, but the complete AI system is not necessarily under local operational control.
This is the difference between data residency and operational sovereignty.
Data residency concerns where information is stored or processed. Operational sovereignty also concerns who can access and control the systems, where essential services operate and what happens when external dependencies become unavailable.
Recent announcements from Google Cloud, Microsoft and IBM, together with an AWS operational exercise, illustrate how providers are addressing different parts of this problem.
1. The six boundaries of sovereign AI
A sovereign AI deployment is not simply a model installed in a local data center.
Consider the document-search assistant. To answer a question, it must authenticate the user, retrieve relevant documents, possibly create or search embeddings, run model inference and record operational events.
Each step introduces a potential dependency.
Data
Where documents, prompts, embeddings, responses, logs and backups are stored and processed.
Storage location alone is insufficient if processing takes place elsewhere. For example, if the assistant sends document content to an external embedding service, locally stored source files do not guarantee local processing.
Model
Where inference runs and whether requests reach external model services.
Control plane
Who can deploy, configure, modify or stop the environment.
If inference runs locally but the control plane requires an external service to remain available, the application has an operational dependency outside its processing environment.
Identity and keys
Who manages permissions, credentials and encryption keys.
A locally hosted application may still depend on remote operational access.
Operations
Who performs maintenance, updates, support, monitoring and recovery.
Determine how updates, monitoring, vendor support and disaster recovery work. Identify any external services required for normal operation or restoration.
Continuity
Which services remain functional if external connectivity or dependencies fail.
If continued operation without external connectivity is essential, test that condition.
| Boundary | What an organization must establish |
|---|---|
| Data | Where documents, prompts, embeddings, responses, logs and backups are stored and processed |
| Model | Where inference runs and whether requests reach external model services |
| Control plane | Who can deploy, configure, modify or stop the environment |
| Identity and keys | Who manages permissions, credentials and encryption keys |
| Operations | Who performs maintenance, updates, support, monitoring and recovery |
| Continuity | Which services remain functional if external connectivity or dependencies fail |
These boundaries are an architectural assessment framework, not a universal legal definition of sovereignty.
They also explain why keeping documents in an approved region does not automatically satisfy an organization’s requirements.
For example, if the assistant sends document content to an external embedding service, locally stored source files do not guarantee local processing.
If inference runs locally but the control plane requires an external service to remain available, the application has an operational dependency outside its processing environment.
Whether those dependencies are acceptable depends on the organization’s specific legal, contractual, security and continuity requirements.
2. What changed in October 2026?
Four developments illustrate different approaches to sovereign infrastructure and AI.
| Provider | Development | What it demonstrates |
|---|---|---|
| Google Cloud | Expanded Google Distributed Cloud air-gapped AI capabilities, including Gemini 3.5 Flash and enterprise search | Local model execution and retrieval within an isolated environment |
| Microsoft | Expanded Sovereign Cloud controls across public, private and customer-operated environments | Workload-specific choices for administration, keys and disconnected operation |
| IBM | Announced a validated architecture combining Sovereign Core and Fusion | Integration of infrastructure and customer-operated governance |
| AWS | Reported results of an October 24 European Sovereign Cloud independence exercise | Testing continued operation without specified global AWS systems |
The developments are not equivalent products or independently established rankings.
Google Cloud: On October 20, Google described Gemini 3.5 Flash on Google Distributed Cloud air-gapped as generally available. Its Gemini-powered enterprise-search experience was in preview. Google says the search workflow keeps indexing, prompts and retrieval within the sovereign perimeter. That is a documented product design, not proof that every deployment automatically meets every sovereignty requirement.
Source: Google Cloud, October 20, 2026
Microsoft: Its October 20 announcement described controls covering operator access, encryption-key management, customer-operated infrastructure and connected or disconnected environments. Features have different maturity levels. External key management with Azure Managed HSM was generally available, while the ability to transition workloads between connected and disconnected operation was entering public preview.
Source: Microsoft, October 20, 2026
IBM: On October 22, IBM announced a validated deployment architecture combining Sovereign Core software with Fusion infrastructure. It aims to simplify the integration of compute, storage, networking and governance for customer-operated environments. Faster deployment and simpler operations are IBM’s stated benefits, not independently demonstrated results for every customer.
AWS: On November 1, AWS reported an October 24 exercise in which its European Sovereign Cloud continued running after two global systems were disconnected. According to AWS, customer workloads remained available.
This was not an air-gap exercise. Traffic normally carried by the AWS global network backbone was rerouted over the public internet. The test supports a narrower finding about independence from specified global systems, not a claim of complete network isolation or resilience under every failure condition.
Source: AWS Security Blog, November 1, 2026
3. What should organizations actually verify?
Return to the regulated organization’s document-search assistant.
Before selecting a sovereign AI platform, its architecture and security teams should trace one complete request: from user authentication to document retrieval, model inference, response generation and logging.
The review should establish where each step executes and which parties can access or administer it.
Four checks are particularly useful.
Verify data movement. Confirm whether documents, embeddings, prompts, responses and logs remain within the required boundary. Storage location alone is insufficient if processing takes place elsewhere.
Verify administrative authority. Identify who can change configurations, access workloads, administer identity systems and manage encryption keys. A locally hosted application may still depend on remote operational access.
Verify operational dependencies. Determine how updates, monitoring, vendor support and disaster recovery work. Identify any external services required for normal operation or restoration.
Test the required failure conditions. If continued operation without external connectivity is essential, test that condition. A vendor’s successful network-backbone isolation exercise cannot substitute for a customer’s test of a fully disconnected application.
The expected evidence may include architecture documentation, configuration records, access logs, contractual commitments and observed test results.
The organization’s requirements determine which evidence matters. Not every system needs to withstand the same failures or prohibit the same forms of external access.
4. Greater independence has operational costs
Stronger sovereignty controls can increase the organization’s operational responsibilities.
An air-gapped AI environment may require dedicated accelerators, local storage, model artifacts, network infrastructure and specialist support.
Software patches and model updates need controlled delivery into the restricted environment. Monitoring, backup and recovery also need to work within the permitted operating boundaries.
Some services available in a connected public cloud may be unavailable or operate differently when disconnected.
These costs matter because maximum isolation is not automatically the best architecture.
An organization whose requirements permit controlled regional cloud services may gain little from maintaining a fully disconnected AI platform.
Another organization handling highly restricted information may have no acceptable alternative.
The decision should follow the requirements, rather than begin with a preferred vendor or a sovereignty label.
5. Sovereignty must be demonstrated, not assumed
The October developments show progress in local AI inference, customer-operated infrastructure, administrative controls and operational independence.
But they address different requirements, and the evidence behind them varies.
A generally available service, a preview capability, a validated vendor architecture and a reported operational exercise should not be treated as equivalent proof.
Generally available
On October 20, Google described Gemini 3.5 Flash on Google Distributed Cloud air-gapped as generally available. External key management with Azure Managed HSM was generally available.
Preview
The Gemini-powered enterprise-search experience was in preview. The ability to transition workloads between connected and disconnected operation was entering public preview. Features have different maturity levels.
Validated architecture
On October 22, IBM announced a validated deployment architecture combining Sovereign Core software with Fusion infrastructure. Faster deployment and simpler operations are IBM’s stated benefits, not independently demonstrated results for every customer.
Reported exercise
On November 1, AWS reported an October 24 exercise in which its European Sovereign Cloud continued running after two global systems were disconnected.
This was not an air-gap exercise. Traffic normally carried by the AWS global network backbone was rerouted over the public internet. The test supports a narrower finding about independence from specified global systems, not a claim of complete network isolation or resilience under every failure condition.
Not equivalent
A generally available service, a preview capability, a validated vendor architecture and a reported operational exercise should not be treated as equivalent proof.
For the organization building the document-search assistant, the practical decision is to define its required boundaries, select an architecture that supports them and verify the controls that matter.
Sovereign AI is a property of the complete deployed system, not simply the country where its data is stored or the label attached to its infrastructure.
References and further reading
- Google Cloud, Enabling the next era of sovereign AI. October 20, 2026.
- Google Cloud, Managed RAG search inside the sovereign perimeter. October 20, 2026.
- Microsoft, Advancing digital sovereignty with greater control and choice. October 20, 2026.
- IBM, IBM Sovereign Core on IBM Fusion simplifies sovereign AI deployment. October 22, 2026.
- AWS Security Blog, Inside a successful AWS European Sovereign Cloud exercise. November 1, 2026.
Source review: November 4, 2026. Product availability and operational claims should be reverified before publication. This article describes architectural considerations, not legal compliance certification.