

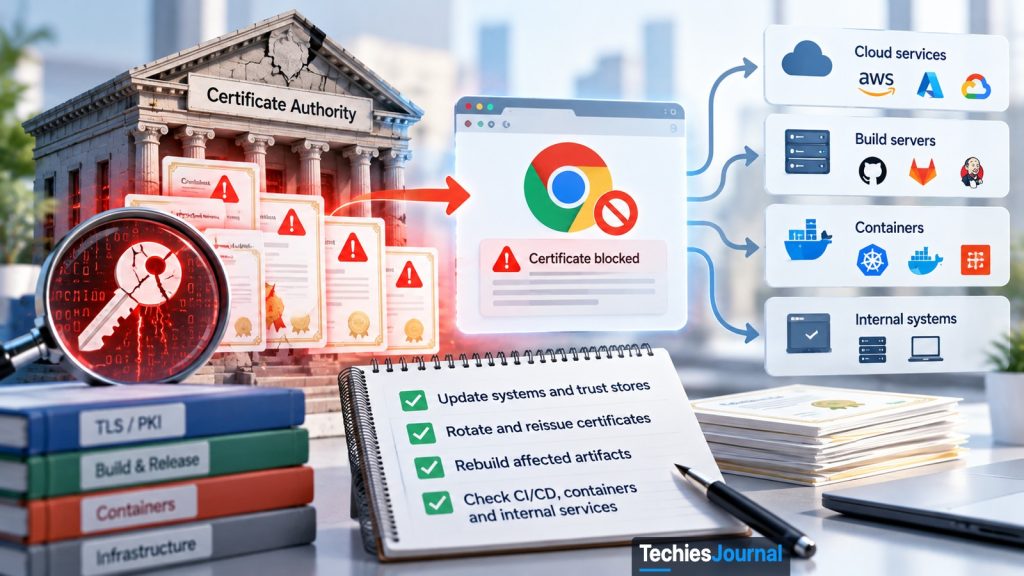
A patched browser is not a patched system
Which of your programs still trust a certificate authority whose keys turned out to be weak?
Before your browser sends anything private to a website, the site has to show a certificate, a signed note saying the server really belongs to that site. The signature comes from a certificate authority, or CA, a company that browsers and operating systems have agreed to trust. In October 2026, a researcher reported that the private keys behind eight signing certificates at one CA, eMudhra, could be recovered.
Chrome and Firefox blocked those keys the same day, and Apple and Microsoft followed over the next days. Go programs, Node.js servers, Python environments and container images do not get that protection automatically. Each needs its own update, and some need a rebuild.
What happened
The report reached Apple, Google, Microsoft, Mozilla and eMudhra on 17 October. The certificates were intermediate CAs. An intermediate CA sits between a trusted root and the certificates websites use. The root signs the intermediate, and the intermediate signs the website certificate. Six of the eight were for website certificates, the kind used by TLS (the protocol behind the browser padlock), and two were for signing code.
A private key should be a very large random number. These were all below 256, so an attacker could simply try every possibility. BleepingComputer, which checked a published key against a revoked certificate, reports that one was just 4. eMudhra says a script error during a key-generation ceremony produced a second, weaker set of keys, and those were chosen for signing by mistake. They dated from April 2025. The company says it found no misuse or breach and revoked the affected CAs within 14 hours.
Chrome blocked the six TLS intermediates within two hours of the report, with an update that needs no restart. Google also removed the root that signed them, emSign ECC Root CA – G3, from the Chrome Root Store. That removal was scheduled for the morning of 27 October, so confirm your Chrome has it. Firefox blocked the certificates on 17 October, and Mozilla decided on 20 October to stop trusting the same root. Apple blocked the certificates on 19 October and the root on 23 October.
Microsoft released out-of-band Windows updates on 26 October that remove seven eMudhra-related certificates from the Windows trust list, aimed at systems that cannot fetch trust updates on their own. Microsoft says it is still reviewing the remaining eMudhra roots.
Google adds that no website certificate from the six intermediates appeared in Certificate Transparency logs, the public records of issued certificates, before the block. Chrome, and Android apps that enforce those logs, would have rejected a forged certificate, which limits the risk for them. Whether anyone used the weakness against other kinds of software is unknown. eMudhra has said it will leave the global TLS certificate business.
What an attacker could do with it
Whoever holds a CA’s private key can sign a certificate for any website, and every program that trusts that CA will accept it. To make use of it, the attacker still has to sit between you and the server, for example on a hostile network. Cloudflare reports no exploitation on its services, and StepSecurity found no report of misuse in build pipelines.
Why one fix does not reach every program
A trust store is the list of CAs a program is willing to trust. Think of the guest list at a building’s front desk. Your operating system keeps one list and your browser may keep another, and the desk checks only its own. Many programs bring a private copy of the list, so they behave the same on every machine.
Say your laptop is fully patched. You run a Node.js script that was built into a container image in September. That script carries its own trust store, so it still trusts the CA, and the laptop’s patch never touches it.
Select a program to see where it gets its trust list and what to do. Every program is also listed below.
The chain being checked: a website certificate, signed by an intermediate CA whose key is recoverable, signed by the emSign ECC Root CA – G3 root. Each program below checks that chain against its own trust list.
Chrome automatic
- Where it gets its list
- Chrome Root Store, plus a blocklist (CRLSet) that Chrome updates without a restart.
- What fixed it
- Blocked the six TLS intermediates within two hours of the report. Removal of the emSign ECC Root CA – G3 root was scheduled for the morning of 27 October.
- What you do
- Confirm Chrome is current. On Android, the equivalent update arrives through Google Play Services and a restart triggers it.
- How to check
- Check the browser version and update status in Chrome’s About page.
Firefox automatic
- Where it gets its list
- Mozilla’s own trust list, plus the OneCRL blocklist.
- What fixed it
- Blocked on 17 October through OneCRL. Mozilla decided on 20 October to stop trusting the same root, and shipped Firefox 158.0.1 and ESR updates for setups that had blocked earlier revocation updates.
- What you do
- Update Firefox. If you block revocation updates, apply the 20 October release.
- How to check
- Check the Firefox version in its About page.
Apple apps automatic
- Where it gets its list
- The system trust store, with Apple’s configuration data sent to devices automatically.
- What fixed it
- Certificates blocked on 19 October, the root on 23 October. Covers Safari, Mail and apps that use Apple’s security frameworks.
- What you do
- Nothing for Safari and Mail. For apps that bring their own list, ask the developer.
- How to check
- Open the app’s update notes, or ask its developer how it checks certificates.
Mac command-line tools not covered yet
- Where it gets its list
- A certificate file on disk, /etc/ssl/cert.pem, read by curl, git, python3, ruby, perl and openssl.
- What fixed it
- Apple says these tools skip its block and revocation checks until a future software update. No fixed version is named.
- What you do
- Administrators can follow Apple’s interim steps and remove emSign ECC Root CA – G3, and optionally AAA Certificate Services. Test afterwards, and repeat the steps if a macOS update replaces the file.
- How to check
- Find out which file each tool reads. Re-check Apple’s notice for the update.
Windows update
- Where it gets its list
- The Windows trust list.
- What fixed it
- Microsoft released out-of-band updates on 26 October that remove seven eMudhra-related certificates, aimed at machines that are offline, cannot reach Microsoft’s trust-update service, or have automatic updates turned off. Microsoft says the same certificates leave Edge’s list on 27 October, and it is still reviewing the remaining eMudhra roots. This comes from BleepingComputer’s report.
- What you do
- Install the update on disconnected systems. Find certificates in your own estate that depend on the removed roots. Windows Server coverage is unconfirmed.
- How to check
- Read Microsoft’s own post for the exact update numbers for your Windows version.
Node.js, Deno, pip update + rebuild
- Where it gets its list
- A trust list bundled with the program: Node.js and Deno ship their own, and pip carries its own copy of certifi.
- What fixed it
- Node.js lists the eMudhra change in its 21 October security releases. Python and pip updates followed, with certifi 2026.10.19. A system update does not change a bundled list.
- What you do
- Update the program, then rebuild any container image that holds an older copy. In Python, upgrade pip in every virtual environment.
- How to check
- Run the version commands in steps 3 and 4 of the one-hour check, and compare with the table.
Go programs rebuild
- Where it gets its list
- The standard library compiled into each Go program.
- What fixed it
- Go 1.27.3 and 1.26.10 shipped on 19 October. Go’s own notice says only “security fixes to crypto/x509”. Other coverage ties them to this incident, so this detail is unconfirmed.
- What you do
- Rebuild each program with the fixed toolchain. Updating Go on the build machine does not change programs that are already built.
- How to check
- Run go version -m on a built program to see which Go version built it.
Apple’s notice shows the same split. The block works automatically in Safari, Mail and apps that use Apple’s security frameworks. Command-line tools that read a certificate file on disk, such as curl, git, python3, ruby, perl and openssl, may keep accepting the certificates until a future macOS update. Apps with their own lists are not covered, and Apple says to ask the developer.
Updating and rebuilding are different jobs. Some programs read their trust store at startup, so a newer file or a restart is enough. In others the fix is part of the program itself. A Go program contains the Go standard library inside the finished file, so fixing the toolchain does nothing for a program built last month. It must be compiled again.
What each tool needs
These fixes appeared from 19 October onward. Check each project’s page before you act, because versions keep moving.
| Tool | What to have | Why it may not be fixed yet |
|---|---|---|
| Go | 1.27.3 or 1.26.10 (19 October) | Go’s notice says only “security fixes to crypto/x509“. Other coverage ties these releases to this incident, so confirm in Go’s release notes. Programs already built keep the old code, so rebuild with the fixed toolchain. |
| Node.js | 22.23.4, 24.22.1 or 26.12.1 (21 October) | Node.js lists “ca-cert (eMudhra Intermediate CA Compromise)” in these releases and ships its own trust store. A system update does not change it, and images with an older Node.js need a rebuild. |
| Python | 3.15.2, 3.14.10, 3.13.18, 3.12.16 or 3.11.18 or newer, with pip 26.2.2, certifi 2026.10.19 and uv 0.13.5 or later | pip carries its own copy of certifi, so each virtual environment needs its own upgrade. 3.11 and 3.12 are source-only releases. Python 3.10 and earlier are end-of-life and got no fix. |
| Rust | rustls-webpki 0.103.16 and webpki-roots 1.0.10 | These are libraries. Everything built on them must be rebuilt and redeployed. |
| Deno | 2.9.8 | Deno ships its own trust store. |
| curl | A CA bundle dated 2026-10-20 or later | The fix is in the bundle file curl reads, so check which file yours uses. |
| Linux distributions | A newer ca-certificates package | Versions differ by distribution. Read your distribution’s notice. |
| Windows | Microsoft’s 26 October out-of-band update | Reported as aimed at machines that are offline, cannot reach Microsoft’s trust-update service, or have automatic updates turned off. Windows Server coverage is unconfirmed. |
| Cloudflare Tunnel | cloudflared 2026.10.2 | Container users must redeploy the fixed image. |
| Docker Desktop, macOS curl | Docker Desktop 4.96.3 or later. No fixed macOS curl version confirmed | Docker’s release notes list the fix in 4.96.1, 4.96.2 and 4.96.3 (21 and 22 October) and say it is rolling out component by component, so keep updating. Apple has named no fixed version for macOS curl, so do not assume coverage. |
Python is the trickiest of these. Python 3.15.1, 3.14.9 and 3.13.17 shipped on 21 October with pip 26.2.2 inside, and later releases followed. A new interpreter does not change the pip inside an old virtual environment, so upgrade pip and uv in every existing one. The patched interpreters also block the compromised keys in the ssl module when verification is on. That is a last line of defence, so still update the trust store.
How deeply to learn this
Know: every developer and IT person should know what a CA is and that some programs keep their own trust store. That is enough to follow the next CA incident.
Use: engineers who build or run software should be able to find which programs and images carry their own trust store, update the ones that read a file, and rebuild the ones that have the fix compiled in.
Master: platform and security leads own the inventory of what runs where, rebuild images on a schedule so fixes do not wait for a release, and decide which tools may rely on the system store.
What you can ignore for now
Skip the advisories for tools you do not run and the certificate counts. Chrome’s figure and a public log index differ by a factor of three, and they measure different things.
A one-hour check
- Your own certificates. If a site of yours uses a certificate that chains to the emSign root, replace it with one from another CA. Google says to do this now. This command shows the immediate issuer:
Look for “emSign” or “eMudhra”, and read the full chain in your certificate tool if unsure.openssl s_client -connect yoursite.example:443 -servername yoursite.example </dev/null 2>/dev/null | openssl x509 -noout -issuer - Go. Run this on build machines:
For a built program, this shows the Go version that built it:go version
Rebuild anything older than 1.27.3 or 1.26.10.go version -m ./yourprogram - Node.js. Run this on servers and inside images:
Update and rebuild anything older than the versions in the table.node -v - Python. In each environment that matters, run these:
Also look for settings that point at an old bundle, such aspython -m pip --version python -m pip show certifiPIP_CERT,REQUESTS_CA_BUNDLEandSSL_CERT_FILE. An old bundle stays in use after you upgrade packages. - Containers. Pull fresh base images and rebuild without the layer cache, for example with
--pull --no-cache, so old layers do not carry the old trust store forward. Then redeploy. - Mac terminals. curl, git and python3 on a Mac may not have Apple’s block yet. Apple’s interim steps for administrators are to remove emSign ECC Root CA – G3, and optionally AAA Certificate Services, from
/etc/ssl/cert.pem. Follow Apple’s notice exactly, test afterwards, and expect to repeat the steps if a macOS update replaces the file. - Certificate errors. If one appears after an update, fix the certificate. Do not turn verification off.
What to do next
Pick one service and trace it. Write down which program makes the secure connection, where it gets its trust store, and who rebuilds it. If nobody owns the rebuild, it will not happen.
A fix in the operating system does not reach programs that carry their own trust store.
What we know and what we do not
| Claim | Type | Source |
|---|---|---|
| Eight eMudhra intermediate CA keys were recoverable: six for TLS, two for code signing | Researcher report, accepted by browsers | Google, Mozilla and Apple notices, and The Hacker News |
| All eight keys were below 256 | Reported | The Hacker News |
| One key was 4 | Reported. BleepingComputer says it checked a published key against a revoked certificate | BleepingComputer |
| Microsoft removed seven eMudhra-related certificates from Windows on 26 October | Reported. Microsoft’s own post not read | BleepingComputer |
| A script error in a key ceremony caused the weak keys | eMudhra statement. Its Mozilla post describes a code flaw that created weaker keys, which were then used by mistake | Digit and Mozilla bug 2083449, comment 11 |
| No misuse, no breach, the keys never used to issue certificates to websites or users, revoked within 14 hours | eMudhra statements, not independently verified | Digit and Mozilla bug 2083449, comment 10 and comment 43 |
| No affected TLS certificate was logged before Chrome’s block | Google statement | Google Security Blog |
| Whether attackers used the weakness against non-browser software | Unknown | StepSecurity |
| About 30,800 unexpired certificates under the root, 99.9 percent via InCommon | Chrome count, as reported | The Hacker News |
| More than 100,000 certificates under the intermediates | Public log index. It showed 107,181 on 29 October and includes probe and test entries | ctlogs.dev |
| Node.js and Python fixed versions | Stated by the projects or a Python-tooling write-up | Node.js release notes and pydevtools |
| Go fixed versions are linked to this incident | Go’s notice names only crypto/x509 fixes. The link comes from other coverage | Go release history |
| Rust, Deno, curl and Linux distribution fixes | Single roundup, not checked against each project | smartscope.blog |
| Docker Desktop and macOS curl fixed versions | Docker Desktop: documented by Docker in 4.96.1 to 4.96.3, rolling out in batches. macOS curl: unknown, no fixed version named | Docker Desktop release notes and Apple Support |
| Chrome’s root removal reached all devices on 27 October | Scheduled, not confirmed | Google Security Blog |
Go deeper
- Google: Protecting Chrome and Android users from compromised eMudhra intermediate CA certificates, for the browser side and the advice to site operators.
- Apple Support: About the compromised eMudhra intermediate CAs, including the command-line tool limit.
- Cloudflare: eMudhra certificate compromise, for
cloudflaredand origin certificates. - The Hacker News: eMudhra to exit global SSL/TLS business, for dates, eMudhra’s statements and the Chrome count.
- BleepingComputer: Mozilla, Google and Apple block compromised eMudhra CA certificates, for the Firefox block and the key value of 4, and BleepingComputer: Microsoft’s Windows updates.
- Digit: eMudhra apologises after weak keys expose 8 intermediate CAs, for eMudhra’s account of the cause.
- Mozilla bug 2083449, where eMudhra and the browser programs discuss the incident.
- ctlogs.dev: eMudhra CA compromise, for the certificate counts from public logs.
- Go release history, for 1.27.3 and 1.26.10.
- smartscope.blog: what to update, a roundup that covers Rust, Deno, curl and Linux distributions.
- Docker Desktop release notes, which list the removal of trust for the eMudhra intermediate CA in Docker Desktop 4.96.1 to 4.96.3.
- Node.js October 2026 security releases.
- Python 3.15.1, 3.14.9 and 3.13.17 announcement and pydevtools: Python updates.
- StepSecurity: effect on pip and CI/CD, for the tools that bundle their own trust stores.
- Related on this site: Node.js Brotli vulnerability, Critical PHP vulnerabilities, and Node.js, Docker and Go changes that break pipelines.
Facts in this article were checked on 29 October 2026. Version numbers and browser actions change quickly, so check the sources above before you act.