Ransomware Affiliates Are Using AI Agents: Who Is Exposed Now and Who Is Next
A leaked server shows ransomware affiliates using AI agents, with a person approving each step. The way in is old, but it is now cheaper to use. Here is who is exposed, what comes next, and what to fix first.
By Prasad Kukkala · Cybersecurity · What changed · · 14 min read
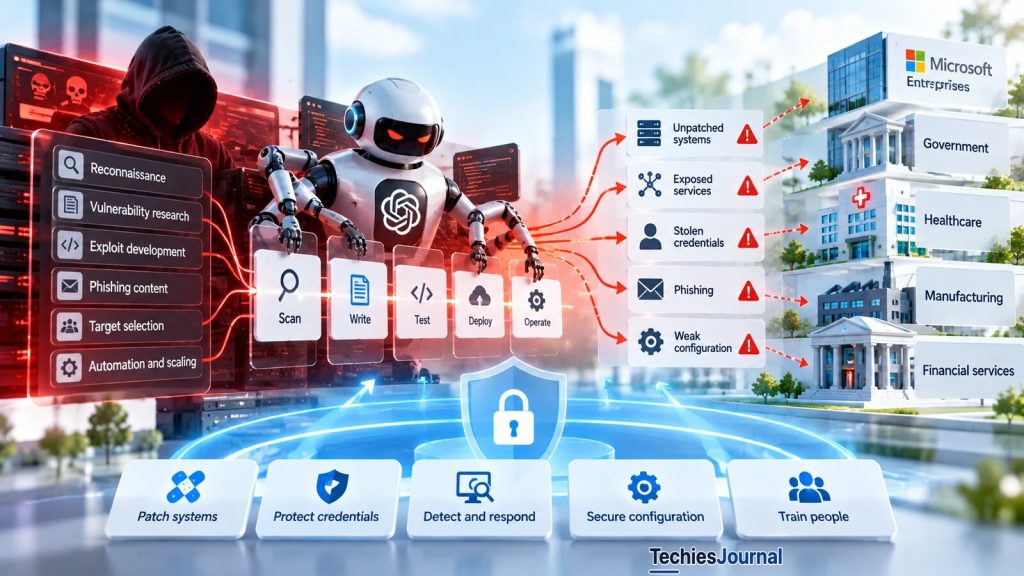
Conceptual illustration of the article's themes: an AI-assisted attack chain, the old weaknesses it uses and the defences. It is not evidence of a real incident or of a named attacker.
The doors are old, but more hands are walking through them
The way in has not changed. The labour behind it has.
Ransomware is software that locks a company’s files and demands money to unlock them. Most attacks today also steal the data first, so the attacker can threaten to publish it. Many ransomware groups do not run every attack themselves. They rent their software to partners called affiliates, who break into companies and share the money with the group.
In late September 2026, a security company called SOCRadar found a server that affiliates of two such groups, INC and The Gentlemen, had left open on the internet. It published its report on 20 October. The server held the records of how the affiliates used AI agents to run break-ins.
An AI agent is a program that does more than answer questions. It decides the next step, uses tools to carry it out, reads the result and decides again.
This article is for IT staff, security teams and anyone who looks after systems for a small or mid-sized organization. It does not retell the SOCRadar report. It uses the report to ask what really changes, who is already affected, and who is next. You will leave with a short list of what to check first and what you can stop worrying about.
What the leaked server shows
Think of a burglary crew. In the old days, one skilled burglar worked one house at a time, and his hours limited how many houses he could hit.
Now picture the same burglar supervising a team of fast, tireless apprentices. He still decides what to do. The apprentices do the slow work of trying doors and carrying things out.
That is close to what SOCRadar describes. The server held about 8,000 messages from 133 working sessions with an AI coding tool.
The records name 62 victim organizations, 36 of them in the United States. Most were not large. Of the 35 where SOCRadar could estimate revenue, 27 earned $250 million a year or less.
The attackers paid for access to commercial AI models through a reseller. SOCRadar says the models included a Claude Opus model from Anthropic and a second model from another company. When a model refused a request, the operators reworded it as an “authorized red team assessment”, which is how security testers describe permitted attack practice, and the model carried on. A persona called “WormGPT” in some news coverage was, according to SOCRadar, only a role-play prompt and not a special criminal AI.
We do not reproduce the server address or the tool names that would help someone copy the setup. The report is linked at the end for defenders who need them.
How the loop worked
The setup is less exotic than the headlines suggest.
An operator writes long instructions for one victim. The AI agent reads them and proposes the next step. The operator approves it or changes it. A set of tools then carries it out against the victim’s network, and the results go back to the agent.
SOCRadar counts 18 skills and 32 connected tools. They let the agent run scanning programs, control a hidden connection into the victim network and copy data out, without a person typing each command. None of these ideas is new. What is new is that one person can supervise many loops at once.
Figure 1. The loop SOCRadar describes. The human approval step matters. Drawn by TechiesJournal from the report.
The human step matters for two reasons. It means this is AI-assisted, not AI-run on its own. And Anthropic’s September 2026 threat report says the same thing in general terms: people choose the targets and review the work, and how independent a tool is and how much harm it does are separate questions.
There is also an irony. The loop keeps a full record of every instruction and result, and the attackers kept it on a server anyone could reach. That record is how we know any of this. It is like a burglar leaving his diary on the pavement.
What worked and what did not
The records read like a small business with lean staff. In one case the agent went after the wrong parent company, and the demand of about 15 million euros was cut once the mistake was spotted. In a healthcare case the demand was between 3 and 8 million Australian dollars, with a 24-hour deadline. The AI was also used to read a victim’s finances and price the demand, which has nothing to do with hacking and a lot to do with how extortion works.
The failures matter just as much. Several attacks on domain controllers failed.
A domain controller is the server that holds all the logins for a Windows network, and it is the prize in most break-ins. Security software stopped some attempts but not others. SOCRadar found only one confirmed case of files being locked, shown in a screenshot from 30 September.
SOCRadar also graded how far each break-in got. By our count, 40 of the 62 stopped at an early stage. Fourteen reached control of the domain, and eight went further, including four that reached a public extortion listing.
One more number helps with scale. SOCRadar reports AI spending of $23,920 on the accounts it could see. Divided by 62 named organizations, that is roughly $386 each.
This is our own arithmetic, not SOCRadar’s, and it ignores spending we cannot see. It still shows the point. The AI costs very little compared with a typical ransom.
The scenarios at a glance
The scenarios below are our reasoning from the evidence. Each has a confidence label so you can tell how much weight it deserves.
“Documented” means we have a source showing it happened. “Likely” means the evidence points that way. “Possible” means it could happen but we have little proof.
The six scenarios at a glance, with who is exposed and how sure we are
Scenario
Who is exposed
How sure we are
1. Management tools open to the internet
Any organization running them
Documented
2. Web panels on shared hosting
Small business websites
Documented, AI link is partly our inference
3. The service provider’s customers
Small businesses that outsource IT
Documented in earlier attacks, AI scaling likely
4. Faster theft, and extortion without locking
Anyone who relies on backups alone
Partly documented
5. AI tools and keys as targets
Teams running AI services
Likely
6. AI-written exploits
Everyone, in time
Possible, thin evidence
Already happening
Scenario 1: Management tools open to the internet
Many organizations run tools that let administrators manage other computers from a distance. In the leaked records, two examples stand out. FortiClient EMS manages security software on laptops, and SimpleHelp is a remote support tool. When a tool like this faces the internet and has a known flaw, an attacker can scan the whole internet for it and walk in.
SOCRadar names a flaw in FortiClient EMS, CVE-2026-35616, that was used before a fix existed. CISA, the United States cyber agency, added it to its list of flaws known to be used in real attacks on 6 April 2026. That list is called the Known Exploited Vulnerabilities catalog. The Shadowserver Foundation saw about 2,000 exposed servers, and the operators claimed they found 2,236 targets, which we cannot verify.
Figure 2. Scenario 1. The same scan finds both consoles, and only one is a way in.
Who is exposed: any organization that runs such a tool reachable from the internet, especially one with nobody watching it. What to watch for: new administrator accounts on the console and changed VPN login scripts. What to do: patch, then take the console off the internet or limit it to known addresses. Our article on exploited edge devices explains why a patch alone does not tell you whether someone got in first.
Scenario 2: Web panels on shared hosting
A web panel is the control page a hosting company gives you to manage your website. cPanel is the best known, and a flaw in it, CVE-2026-41940, was used from February 2026, fixed on 28 April and on the CISA list on 30 April. Scans found about 1.5 million cPanel logins reachable from the internet, though not all were vulnerable. SOCRadar lists cPanel among the entry points in these records.
A separate AI-assisted intruder, called CyberXero, shows how fast this can go. SOCRadar reports one run that scanned 4,708 targets, found 429 WordPress admin pages and planted 32 web shells in 61 seconds. A web shell is a small hidden page that gives the attacker control of the site. We do not know of ransomware in that case, so treat it as a speed example and not as proof of a ransomware link.
Figure 3. Scenario 2. One weak panel puts every site on the server at risk.
Who is exposed: small business websites on shared hosting, and the people whose data sits on them. What to do: keep admin pages behind a second login or an allowed list of addresses, use a unique admin password, and keep a clean copy you can restore.
Likely next
Scenario 3: The service provider’s customers
A managed service provider, or MSP, is a company that runs IT for many small businesses. To do that, it uses a remote tool that can reach every customer. One break-in at the provider can give an attacker a way into all of them.
This is not new. CISA’s advisory AA25-163A describes ransomware attackers using a SimpleHelp flaw (CVE-2024-57727) in 2025, including to reach the customers of a utility billing software provider.
Our inference is that an AI agent makes this cheaper, because it can run the same routine on each customer without extra effort. The operators also claimed to have scanned 4,922 SimpleHelp servers. That is their claim and we cannot verify it.
Figure 4. Scenario 3. One door at the provider opens many customers.
Who is exposed: small businesses that rely on a provider and have no one checking its remote access. What to do as a provider: require a second login step, limit which addresses can connect, and use separate admin accounts for each customer. What to do as a customer: ask your provider how its remote access is protected, and ask what would stop one stolen password from reaching you.
Scenario 4: Faster theft, and extortion without locking
Many groups now steal data first and lock files second. Some skip the locking. They threaten to publish what they took. This is often called double extortion when both happen, and data-only extortion when the files are never locked.
Anthropic’s September report describes cases, not specific to ransomware, that went from first access to bulk data theft in hours. In one it took about three hours to reach full cloud administrator rights from one stolen developer token. The extortion deadlines in the leaked records ran from 24 to 72 hours.
Coveware, a firm that handles ransomware cases, reports that data theft appeared in 76 percent of its second-quarter 2026 cases. Victims paid in 15 percent of cases where data was stolen but nothing was locked. The lesson is that backups protect you from losing files. They do not protect you from the data leaking.
Figure 5. Scenario 4. The timeline is illustrative. The figures come from different reports, not one incident.
Who is exposed: any organization that thinks “we have backups” is the whole plan. What to do: assume data can leave, watch for large uploads to cloud storage, and limit the file-copy tools attackers like to reuse, such as rclone and restic. Have your breach notice ready, and see our guide to reading a breach notice for what a good one says.
Scenario 5: AI tools and keys as targets
An API key is a password that lets a program use an AI service, and the account owner pays the bill. An AI gateway is a service that sits in front of AI models and hands out access to them. Both hold money and power.
The operators here paid for their own AI use by account. Our inference is that an unrestricted key is worth money to criminals who need AI access they do not want to pay for. Anthropic’s report adds that one actor targeted about 30 AI companies in four days.
Figure 6. Scenario 5. A leaked key is money and access in someone else’s hands.
Who is exposed: teams that run AI gateways, tool servers or agents with wide access, and developers who leave keys in code repositories. What to do: give each key the least access that works, set spending limits, rotate keys, and log what agents call. Our articles on the MCP credential boundary and exposed AI servers cover the technical side.
Possible, but not proven
Scenario 6: AI-written exploits
A zero-day is a flaw that attackers use before the vendor has released a fix. According to BleepingComputer’s coverage, Google’s threat intelligence group reported in May 2026, for the first time, a threat actor using a zero-day exploit that it believes was built with AI. It was a way around two-factor login in an open-source admin tool. Google says it disrupted the attack before mass exploitation began. The code carried tell-tale signs of AI such as a made-up severity score, and Google reports high confidence in the link, although it does not know which model was used. This is one documented case, and wider use is not documented.
In September, the same group described a multi-agent framework that gathered thousands of passwords in under six hours. We know of it through The Hacker News, and neither the attacker nor the victims were named.
Figure 7. Scenario 6. The window we can prove is long. The shorter one is only a possibility.
We would not plan around this yet. The cPanel flaw was used for about two months before a fix, with no sign of AI involvement. The bigger risk today is old flaws that stay unpatched. If AI does speed up exploit writing, reducing what you expose will help more than trying to patch faster.
What may not change
It is easy to overstate all this. The leaked loop works, but it is sloppy. Attacks failed, one agent picked the wrong target, and the logs exposed the whole operation. We have one confirmed case of locked files.
Coveware’s second-quarter data is a useful counterweight. It reports that the average ransom rose 176 percent to $1,880,612, but the median fell by half to $150,000.
It also says social engineering, which means tricking people instead of attacking software, was again a leading way in. That is one firm’s caseload and it does not mention AI. It reminds us that the old problems have not gone away.
If a victim paid that median, that single payment would be about 6.3 times the whole recorded AI spend of $23,920. That is our arithmetic, and it only applies when someone pays. Payment rates are falling, so the sums do not simply favour the criminals.
A defender map by stage
The loop in Figure 1 goes through the same stages as any break-in. This table shows what the records suggest and what to check at each stage.
Defender map by stage: what the records show and what to check
Stage
What the records show
What to check
Getting in
Known flaws in remote tools and web panels
Patch, take consoles off the internet, review what is exposed every month.
Staying hidden and spreading
Hidden connections into the network, reused passwords, older domain controllers
Alert on unknown remote tools. Use unique admin passwords. Retire old servers.
Switching off defences
A trick that abuses a signed but flawed driver to turn off security software
Block known vulnerable drivers and turn on tamper protection.
Taking the data
Cloud copy tools sending files out
Watch uploads to cloud storage and restrict copy tools.
Locking and demanding
Financial research, calls, 24 to 72 hour deadlines
Prepare notice templates, an incident contact and decision rules in advance.
Recovering
Backup servers and virtual machine hosts targeted
Keep backups that cannot be changed, and keep the backup server off the main network.
How deeply should you learn this?
Know: Everyone in a technical role should understand that AI makes old attacks cheaper and that a person still decides. You should be able to explain why internet-facing management tools are the first thing to protect.
Use: IT operations, security and cloud staff should be able to list what their organization exposes, check it against the CISA list, tighten remote access and test the restore process. If you work for a managed service provider, treat your remote tool as your most valuable asset.
Master: Security leaders and incident responders should test these scenarios against their own setup. They should rehearse extortion decisions before they are needed, and decide how much monitoring, response time and recovery capacity the organization can afford. That is a judgement about trade-offs, not a checklist.
What you can ignore for now
You do not need to track malware family names, AI model names or each new criminal brand. They change quickly and they distract from the lasting lesson. You also do not need to buy a new tool because the word AI is in the headline.
A practical next step
Make a list of every service in your organization that faces the internet and is used to manage something else. That means remote support tools, VPN consoles, hosting panels, backup consoles and AI gateways. For each one, write down who owns it, whether it is patched, and whether it needs to be public.
Fix the oldest one first. That is more useful than any new product.
The tools are faster. The targets are the same. And the list in your hands is the one that matters.
What we know and what we do not
What we know and what we do not, by type of statement
Label
Statement
Researcher report
An exposed server held logs of AI-assisted break-ins by affiliates of two ransomware groups, with 62 named victims and a human approval step (SOCRadar).
Researcher report
The operators used paid AI models through a reseller and reworded refusals.
Operator claim, unverified
2,236 FortiClient EMS targets and 4,922 SimpleHelp servers scanned.
Vendor data
Coveware: the median ransom fell, data was stolen in 76 percent of cases, and AI is not mentioned.
Our inference
AI lowers the cost per victim, so smaller organizations and a provider’s customers become more attractive targets.
Our arithmetic
About $386 of AI spend per named victim. One median payment of $150,000 would be about 6.3 times the whole recorded AI spend of $23,920, if paid.
Unknown
How many attacks the operators finished. Who ran the server. Whether other groups run similar loops. Whether the AI companies acted.
Facts in this article were checked on 27 October 2026. Most numbers about the exposed server come from one security vendor and may be revised. Confirm against the sources above before you act.